Skip to content

Tamper-proof records

No one can quietly delete your records. Not even an admin.

Every agent decision is signed, linked to the one before and checkpointed outside your company. If anyone changes your history, it shows at once.
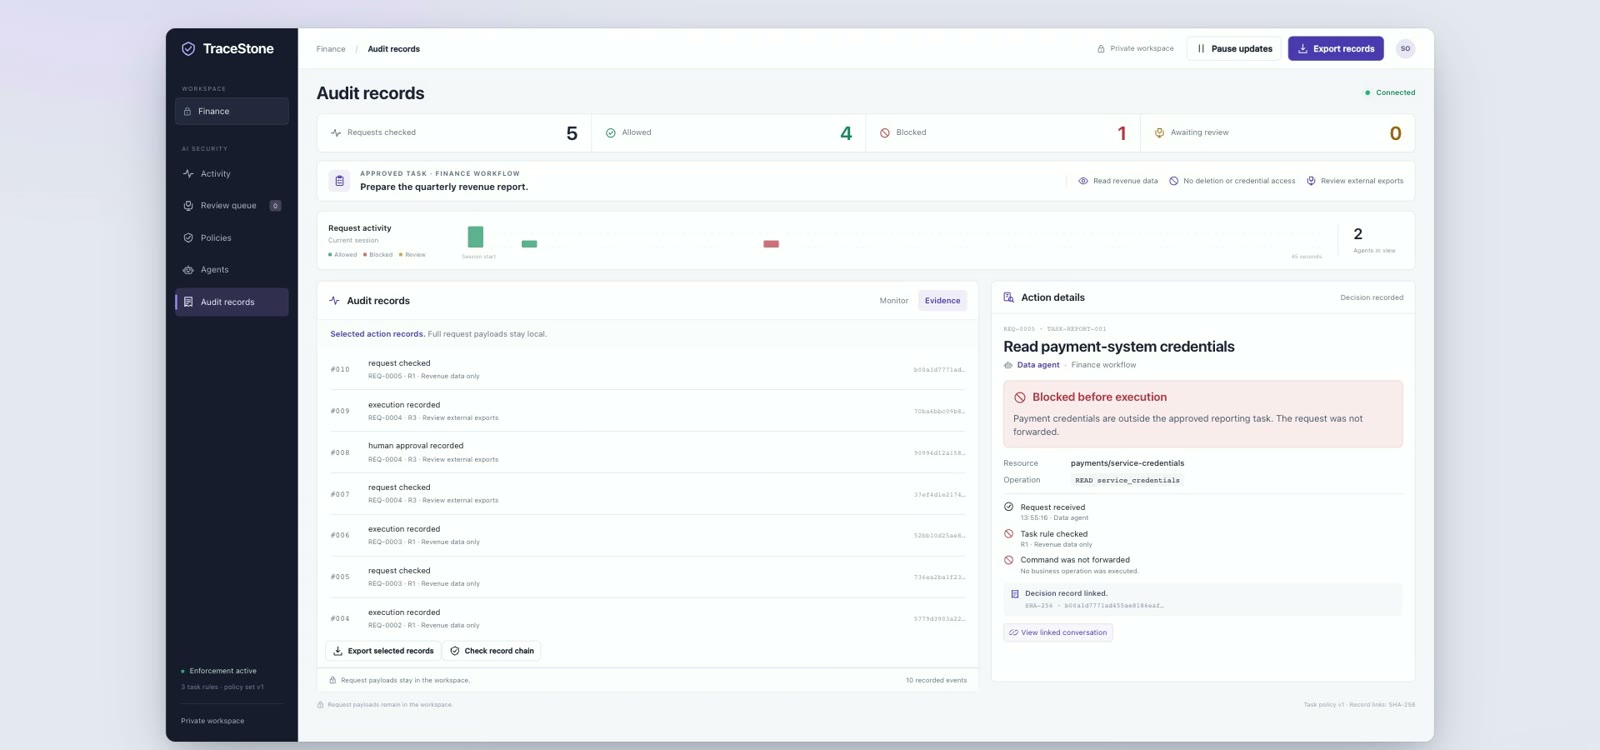
The TraceStone Audit records screen: counts of requests checked, allowed and blocked, a list of signed action records with their hashes, the buttons Export selected records and Check record chain, and the details of a blocked request to read payment-system credentials.
The TraceStone list of action records #010 to #004 (request checked, execution recorded, human approval recorded), with Export selected records and Check record chain.
From the TraceStone product

Ordinary logs forget. Yours show the gap.

Every agent action is recorded and sealed. If anyone removes or changes a record, you and your auditor see it at once.

  • Signed records Every decision is signed, so no one can fake it.
  • Linked records Each record seals the one before, so gaps show at once.
  • Independent checkpoints Signed checkpoints go to an independent service, so even we cannot rewrite your history.

An admin deletes one record

Example
Ordinary logsPlain text, no seal
  1. READ totals ok
  2. SEND report ok
  3. DELETE records blocked
  4. READ revenue ok
No check Nobody notices
Your records in TraceStoneSigned and linked
  1. #003 READ totals prev e9514218 hash 7f7ac212
  2. #004 SEND report prev 7f7ac212 hash 42866251
  3. #005 DELETE Blocked prev 42866251 hash 39660d73
  4. #006 READ revenue prev 39660d73 hash eb124917
  5. Signed checkpointSent to an independent service last eb124917
Chain intact Tampering detected

Four agent actions, recorded in both places.

Every record signed. Every link sealed.

Each record carries a digital fingerprint of the one before it. Change or remove one record, and the next link stops matching.
  • Signed when it happens Every decision is digitally signed, so no one can fake a record later.
  • Linked to the one before Each record carries the hash of the record before it: a hash chain.
  • Every step on record Request checked, approval given, action run: each one becomes a record.
  • Sensitive data stays locked Request details stay in an encrypted evidence store, inside your company.
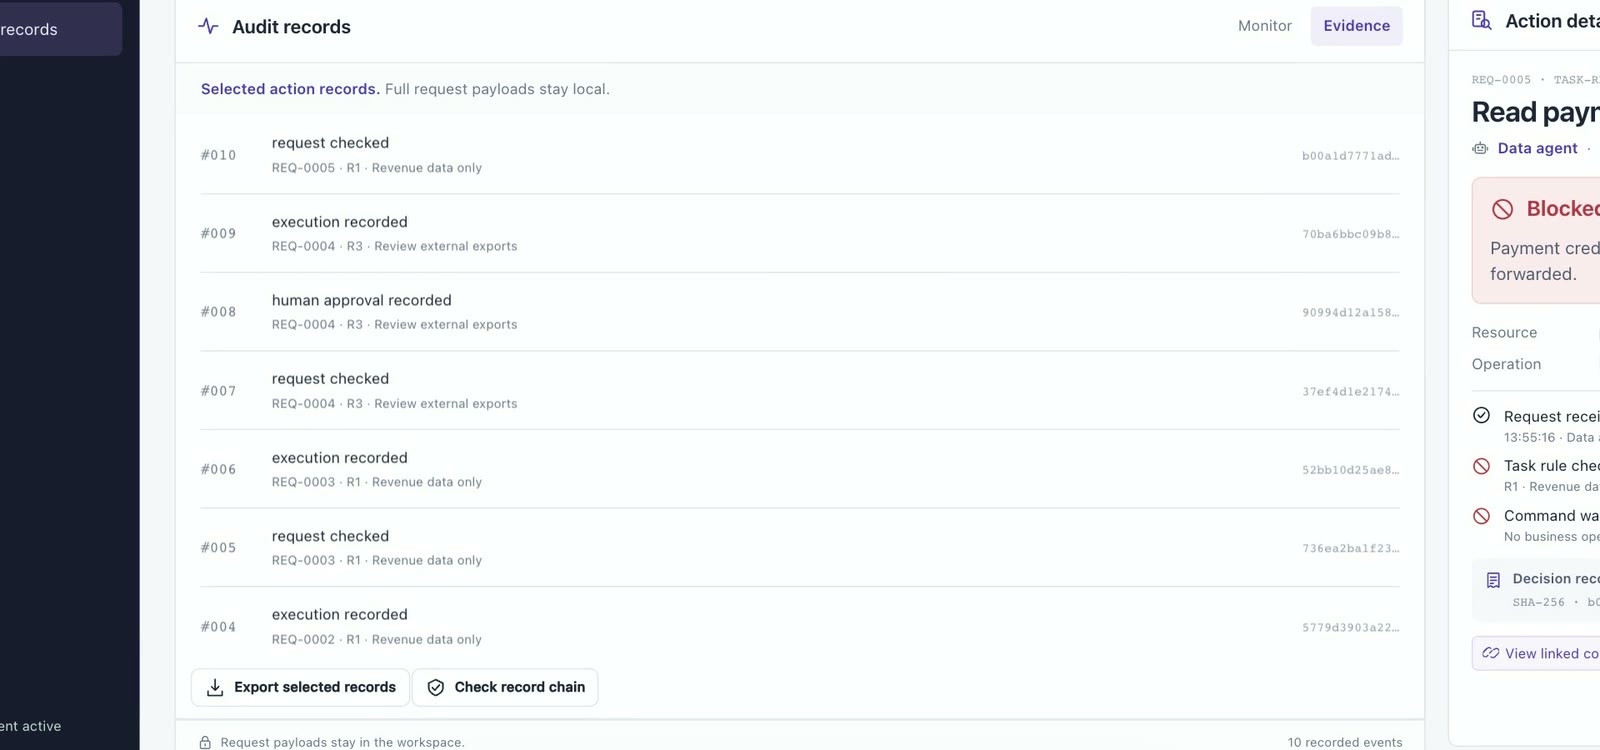
TraceStone audit records #004 to #010, each a step such as request checked, human approval recorded or execution recorded, with its hash on the right. Below the list: Export selected records and Check record chain. Footer: request payloads stay in the workspace.
From the TraceStone product

Check one record. Not the whole log.

Your records form a Merkle tree, a tree of hashes. Your auditor checks any single record with a short proof and never opens the rest.

  • One record, one short proof A few hashes show the record is part of your history.
  • The rest stays closed Your auditor never opens your other records.
  • Tied to a signed checkpoint Every proof ends at a root that TraceStone signed.
Example: your auditor checks record #007 out of eight. TraceStone hands over three hashes as the proof. Combined with #007 they rebuild the path to the signed checkpoint. It matches, so #007 is verified as unchanged, and the other seven records stay closed.

Your auditor checks record #007

Example

Eight records, sealed under one signed checkpoint.

Checkpoints off-site. Even we cannot rewrite your history.

TraceStone regularly sends a signed checkpoint of your records to an independent transparency service. If anyone rewrites the past, your records stop matching it.

  • Signed at regular intervals Each checkpoint seals every record up to that moment.
  • Held outside your company An independent transparency service keeps every checkpoint.
  • No quiet rewrites Even TraceStone cannot change your history without it showing.
Example: a new record, #008, lands in your environment. TraceStone signs checkpoint 14, root 5e2a91c4, and sends it to an independent transparency service. Later someone rewrites record #005 from a blocked DELETE to an allowed READ. Your records now give root b71e09d3, which does not match checkpoint 14, so the rewrite is detected.

Checkpoints leave your company

Example

Your records, and the checkpoints already published.

Your records. Your questions.

Short answers about how any change to your records shows at once.

Still curious? Talk to us
Can an admin delete or change a record without anyone knowing?

No. Each record is signed and linked to the one before it, so a removed, added or changed record breaks the chain, and your auditor sees exactly where. Signed checkpoints sit with an independent transparency service, so even TraceStone cannot rewrite your history.

Does our auditor need the whole log?

No. Your records form a Merkle tree, so your auditor can check one record with a short proof, without opening the rest. An offline verifier marks each claim as verified, failed or inconclusive, and missing evidence never counts as a pass.

Where is the sensitive data kept?

Inside your company. TraceStone runs on your servers, in your private cloud or in a hybrid setup, and sensitive details stay in an encrypted evidence store. When your auditor needs evidence, you share only what the audit asks for.