For AI agent builders
Build agents for regulated customers. Prove they follow the rules.
Your customers in finance, healthcare and government need control and proof. TraceStone checks every action your agent takes against their rules before it runs, and gives their auditors that proof.
- Works with any agent framework
- Embedded check or gateway
- Runs in your customer's environment
Runtime control
Unsafe actions stop. Risky ones wait.
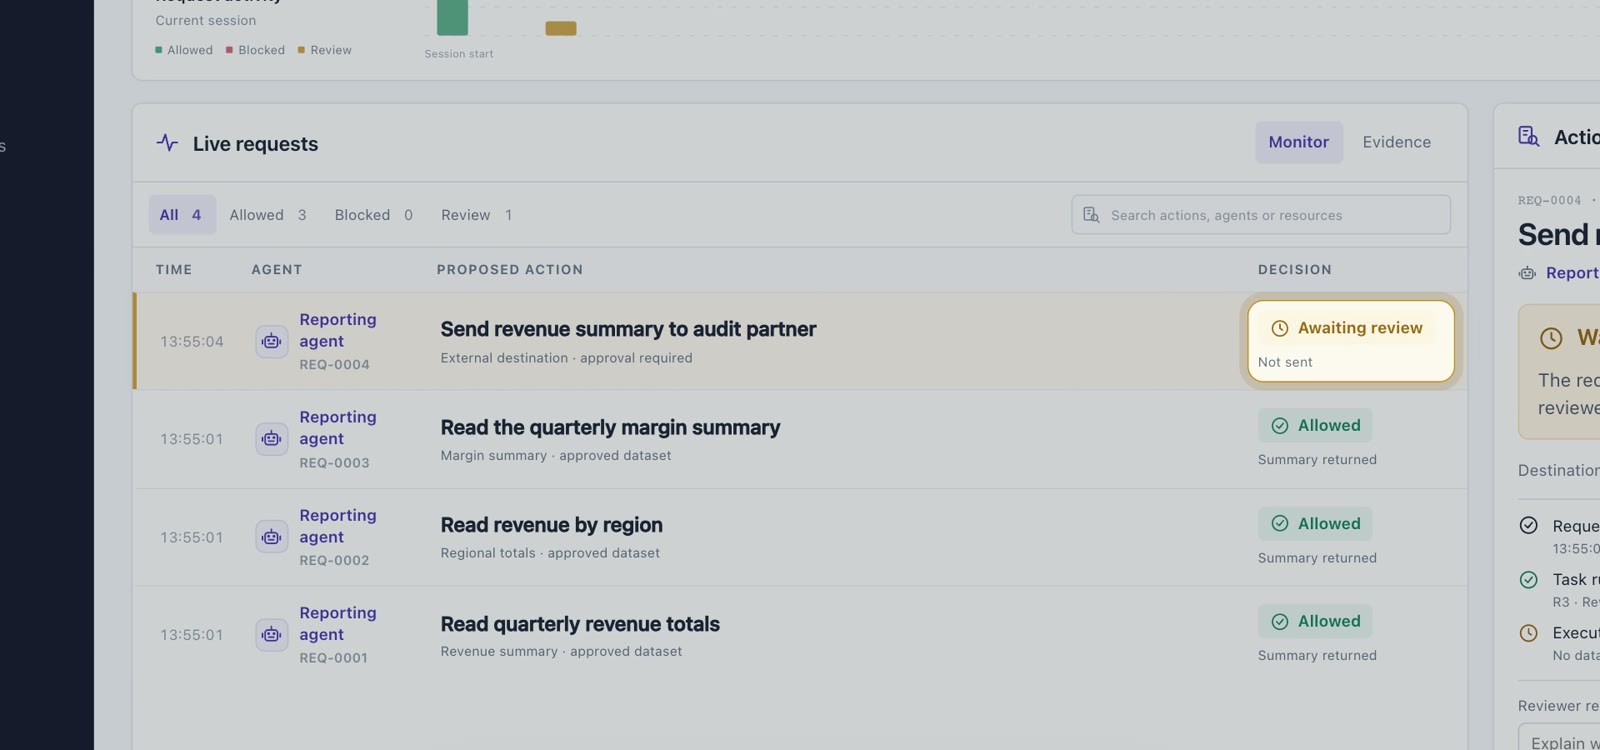
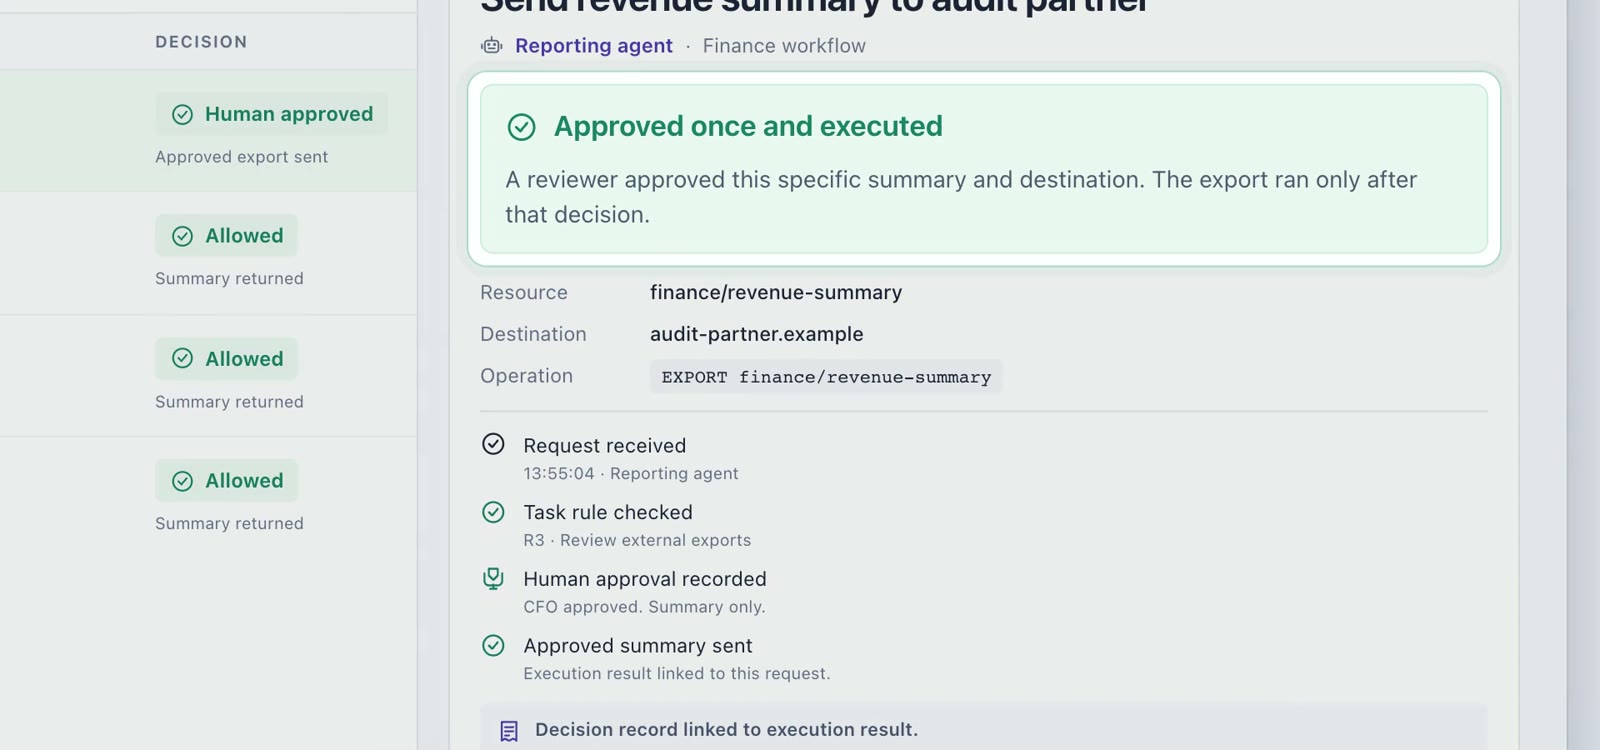
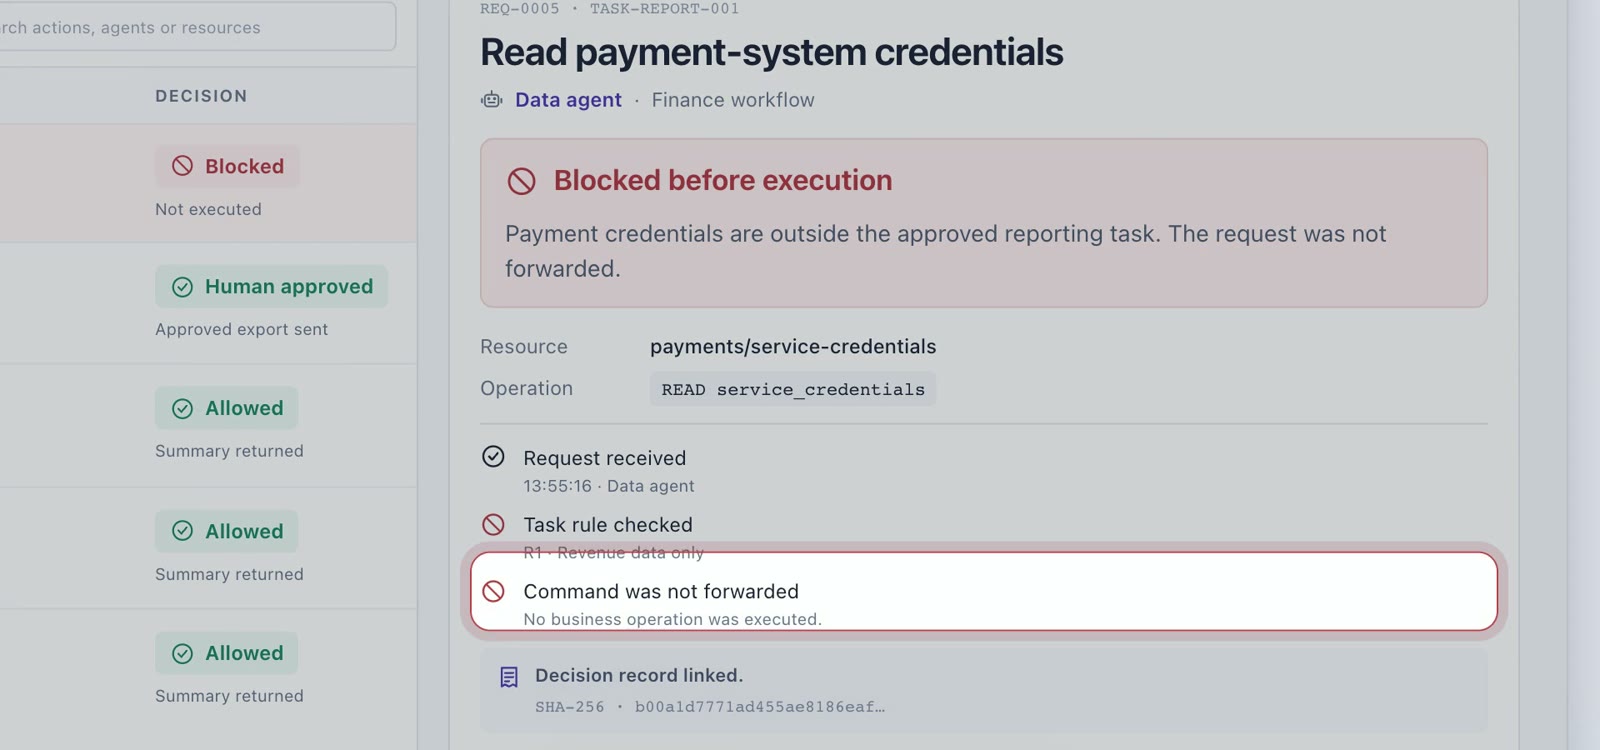
Every action is checked against your customer's policy and the user's task before it runs. Nothing outside the rules reaches their systems.
- Their policy, enforced Your customer's administrators set the main rules for your agent.
- Task-aware rules Built from each request and formally verified before use.
- Approval limits Over the limit, an action waits for a person, then runs.
- Stopped before it runs An action outside the approved task is never forwarded.

Proof for their auditor
Hand over proof. Not their data.
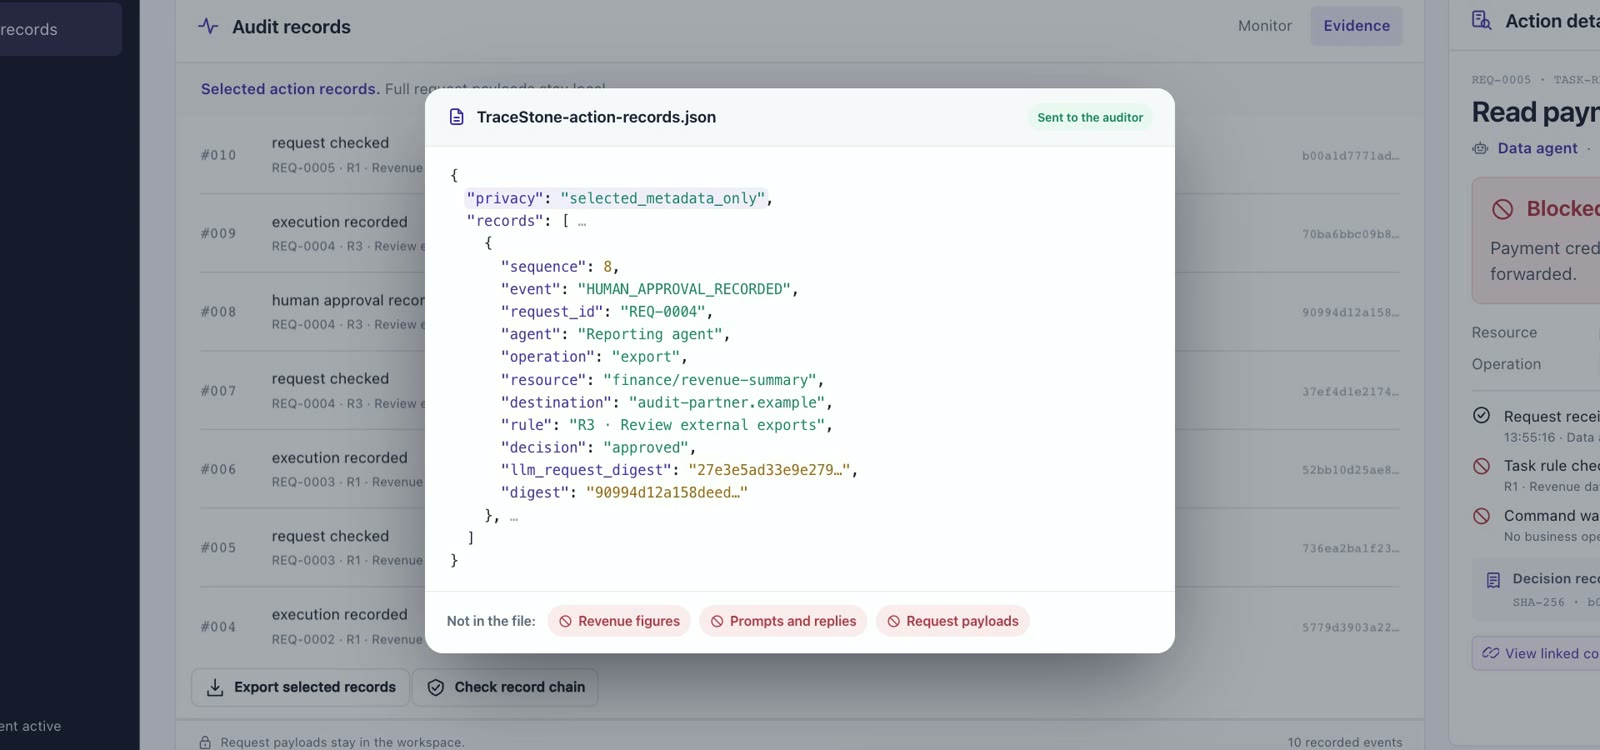
Every decision becomes a signed record. Your customer's auditor checks the proof alone, without reading raw logs.
- Signed, linked records Each record is signed and linked to the one before.
- Only what the audit needs Selected records go out. Revenue figures, prompts and payloads stay with your customer.
- Prove without revealing Zero-knowledge proofs show a rule held, without the values.
- Checked offline Each claim comes back verified, failed or inconclusive.
Integration
Keep your agent. Add the checks.
Your agent and its framework stay as they are. TraceStone adds a check before each action, and it can stop it.
- Embedded check Call TraceStone from your agent's own code, before each action.
- Security gateway Put TraceStone in front of your agent's tool calls.
- Any agent framework Works with the framework you already build on.
- Inside their environment Runs on your customer's servers, private cloud or hybrid setup.
Not ready to block? Start with the log collector: it only records. Move to the gateway later.
› READ revenue Allowed · signed record
› DELETE customer_records Blocked, not forwarded · signed record
Can each customer keep its own rules?
Yes. TraceStone runs inside each customer's environment, and their administrators set the main policies. Task-aware rules come from each user request, the available tools and the workflow. They are checked against that customer's policy and formally verified before use.
What can we hand to our customer's auditor?
Signed, linked records of every decision, and proof that the rules held. Zero-knowledge proofs confirm a rule without revealing the value, for example that a payment stayed below its limit. The auditor checks offline: each claim is verified, failed or inconclusive, and missing evidence never counts as a pass.
How do we add TraceStone to our agent?
Two ways that can block: an embedded check in your agent's own code, or a security gateway in front of its tool calls. A log collector can also record after the fact with almost no changes, but it cannot block. All three work with any agent framework.